Solutions/Content governance
Regain control of your document estate
Your retention rules already exist. So do your regulatory obligations. Yet content stays fragmented across document management systems, archives, email platforms, network drives and business applications.
Document governance should not depend on manual investigation
Within a fragmented document estate, every request becomes an investigation. Teams must locate the relevant information, verify its context, identify sensitive data, determine which rules apply and demonstrate what action has been taken.
A personal data access request arrives
Teams locate the relevant information and verify its context before they can answer.
An auditor asks about your retention
You have to show that the policy has been applied correctly, not that it exists.
A new regulatory requirement lands
All affected content must be identified quickly, wherever it sits.
Sensitive data circulates across systems
Documents keep accumulating, and archiving policies stay largely theoretical.
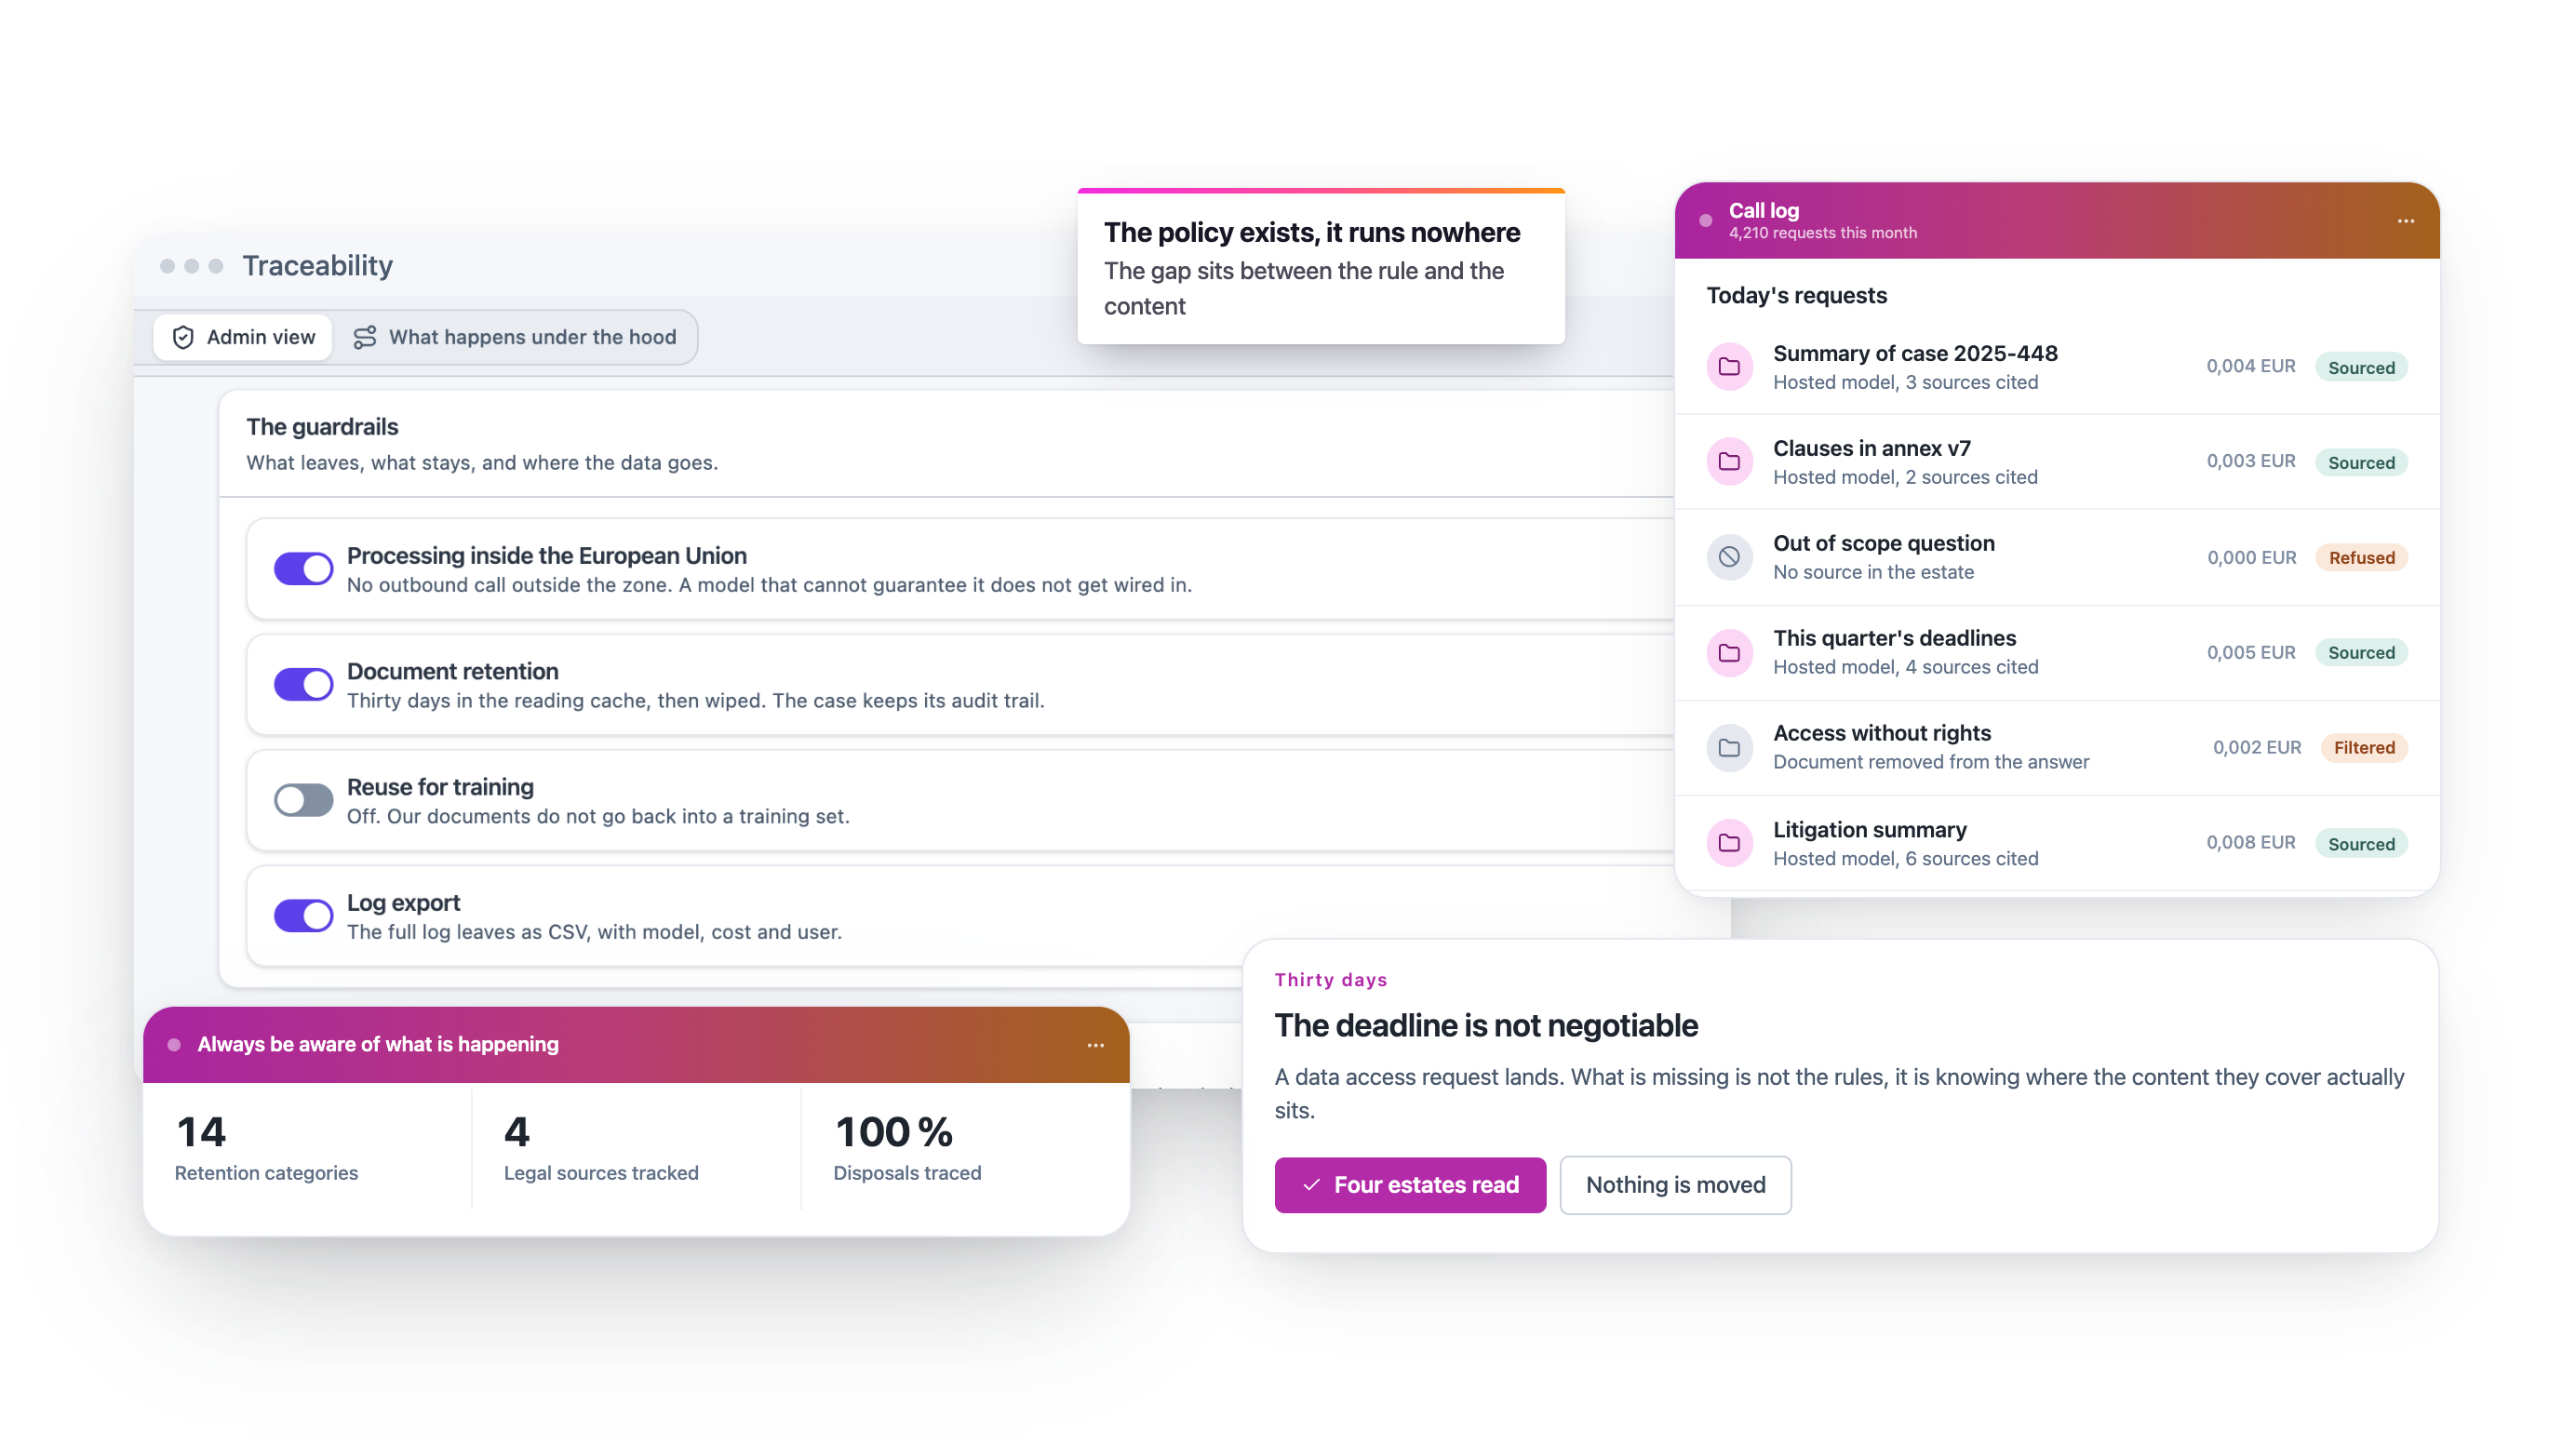
The problem is not the absence of rules. It is the gap between the rules that have been defined and the reality of the content itself.
End-to-end governance, from classification to evidence
Uxopian Software turns document governance into an operational capability. You classify, protect, retain, dispose of and audit content inside your existing environments.
Understand what your document estate actually contains
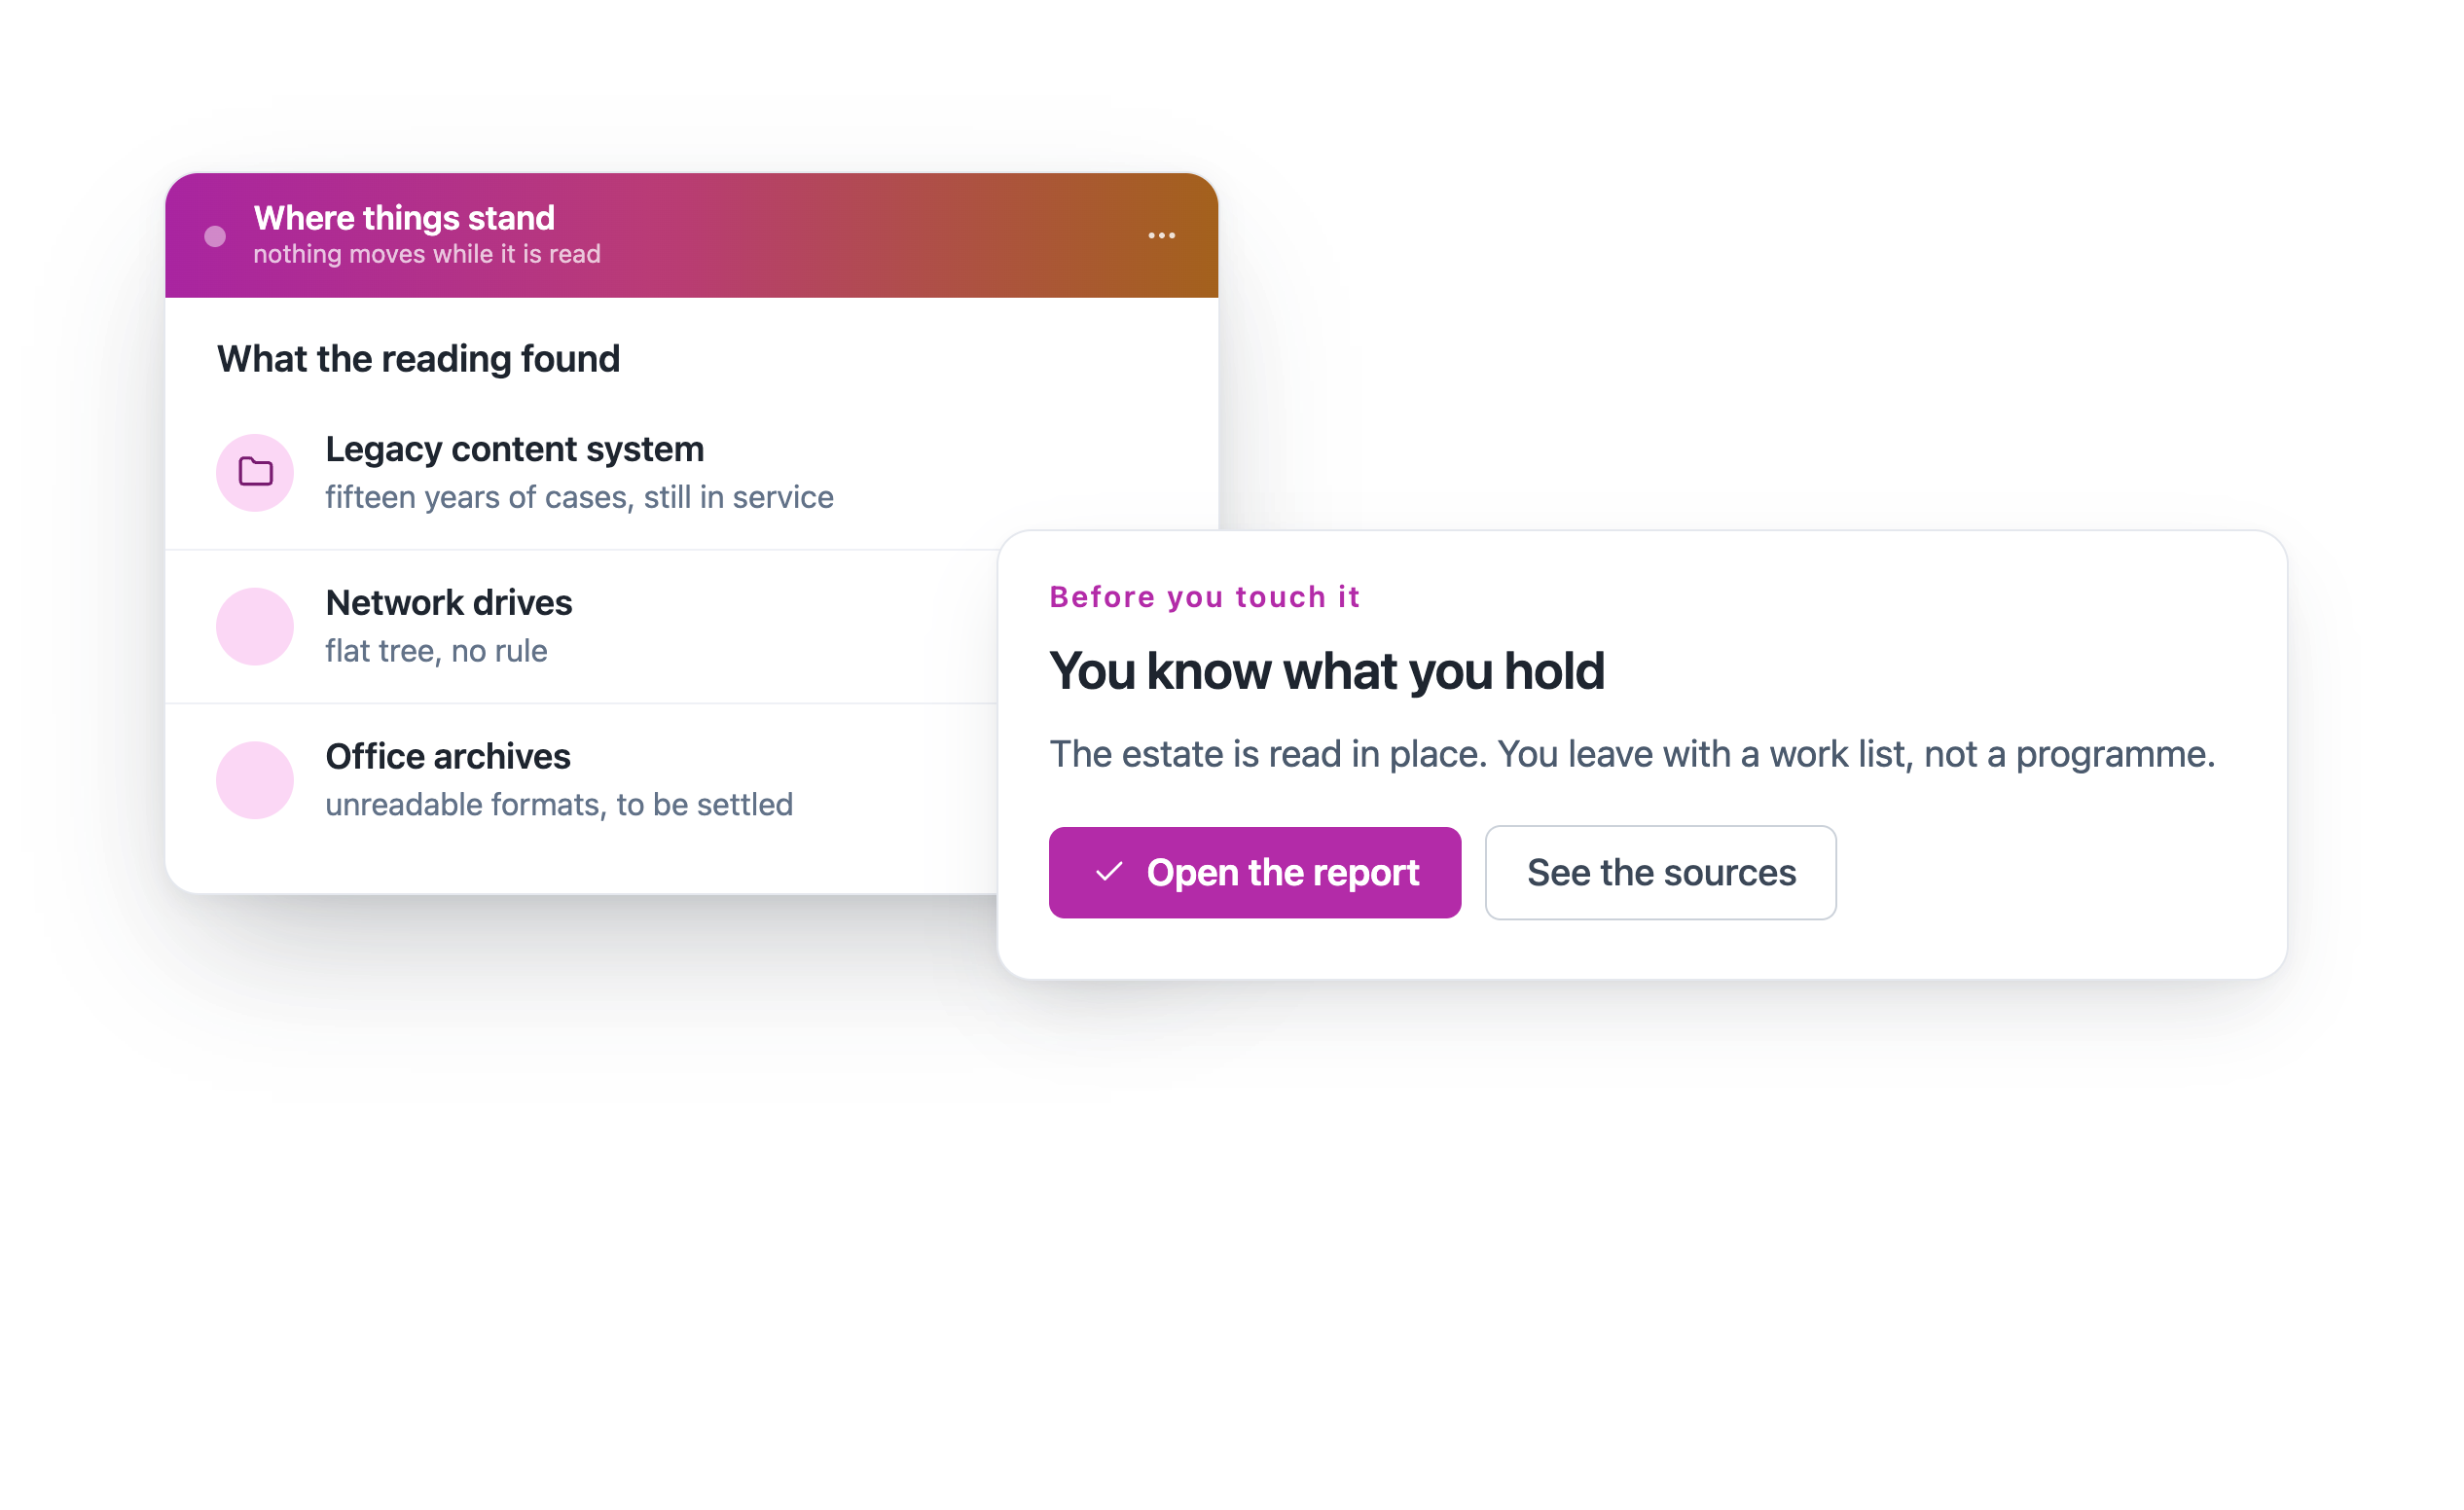
Before content can be governed, it must first be visible. Content held across your different systems is analysed and classified by type, sensitivity, business value or retention period. The objective is not to move your data into a new platform, it is to make it usable where it already resides.
Put your retention policies into practice
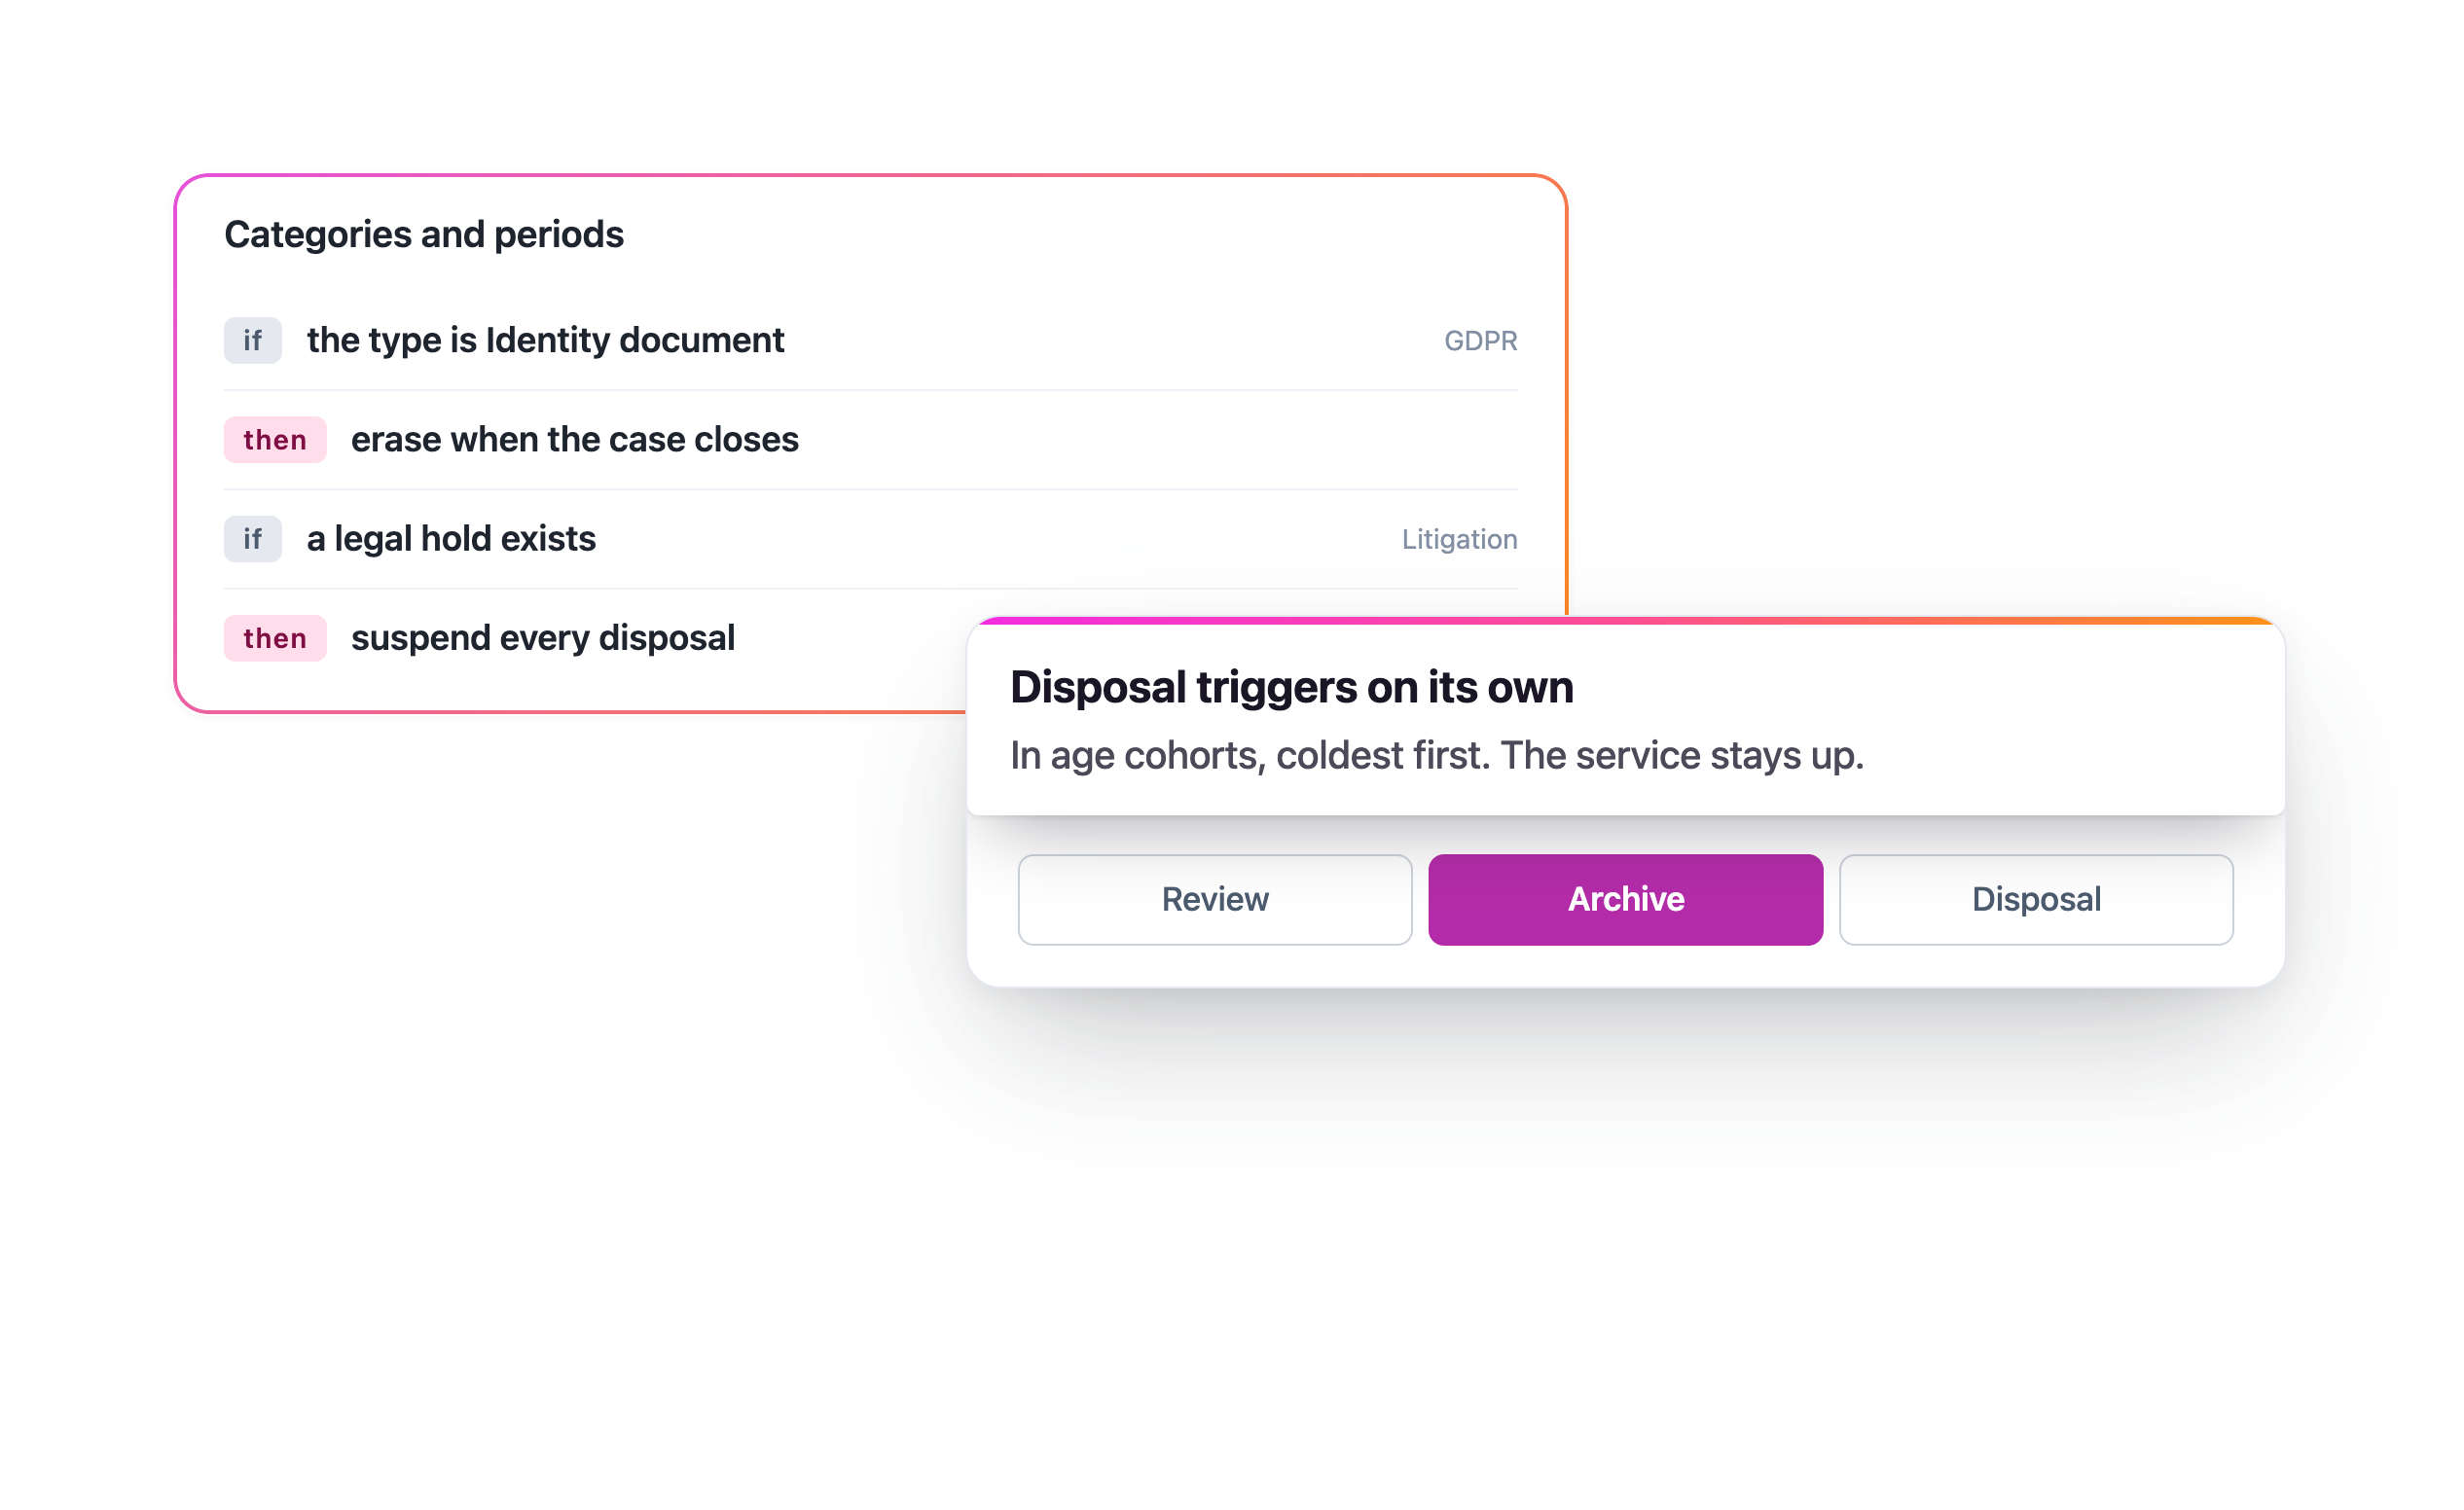
A retention policy does not protect an organisation while it remains confined to a spreadsheet. Rules connect to the content they govern: at a defined milestone, a workflow initiates a review, an archival action, a secure deletion or an extension. A legal hold suspends the planned action.
Protect sensitive data without losing its context
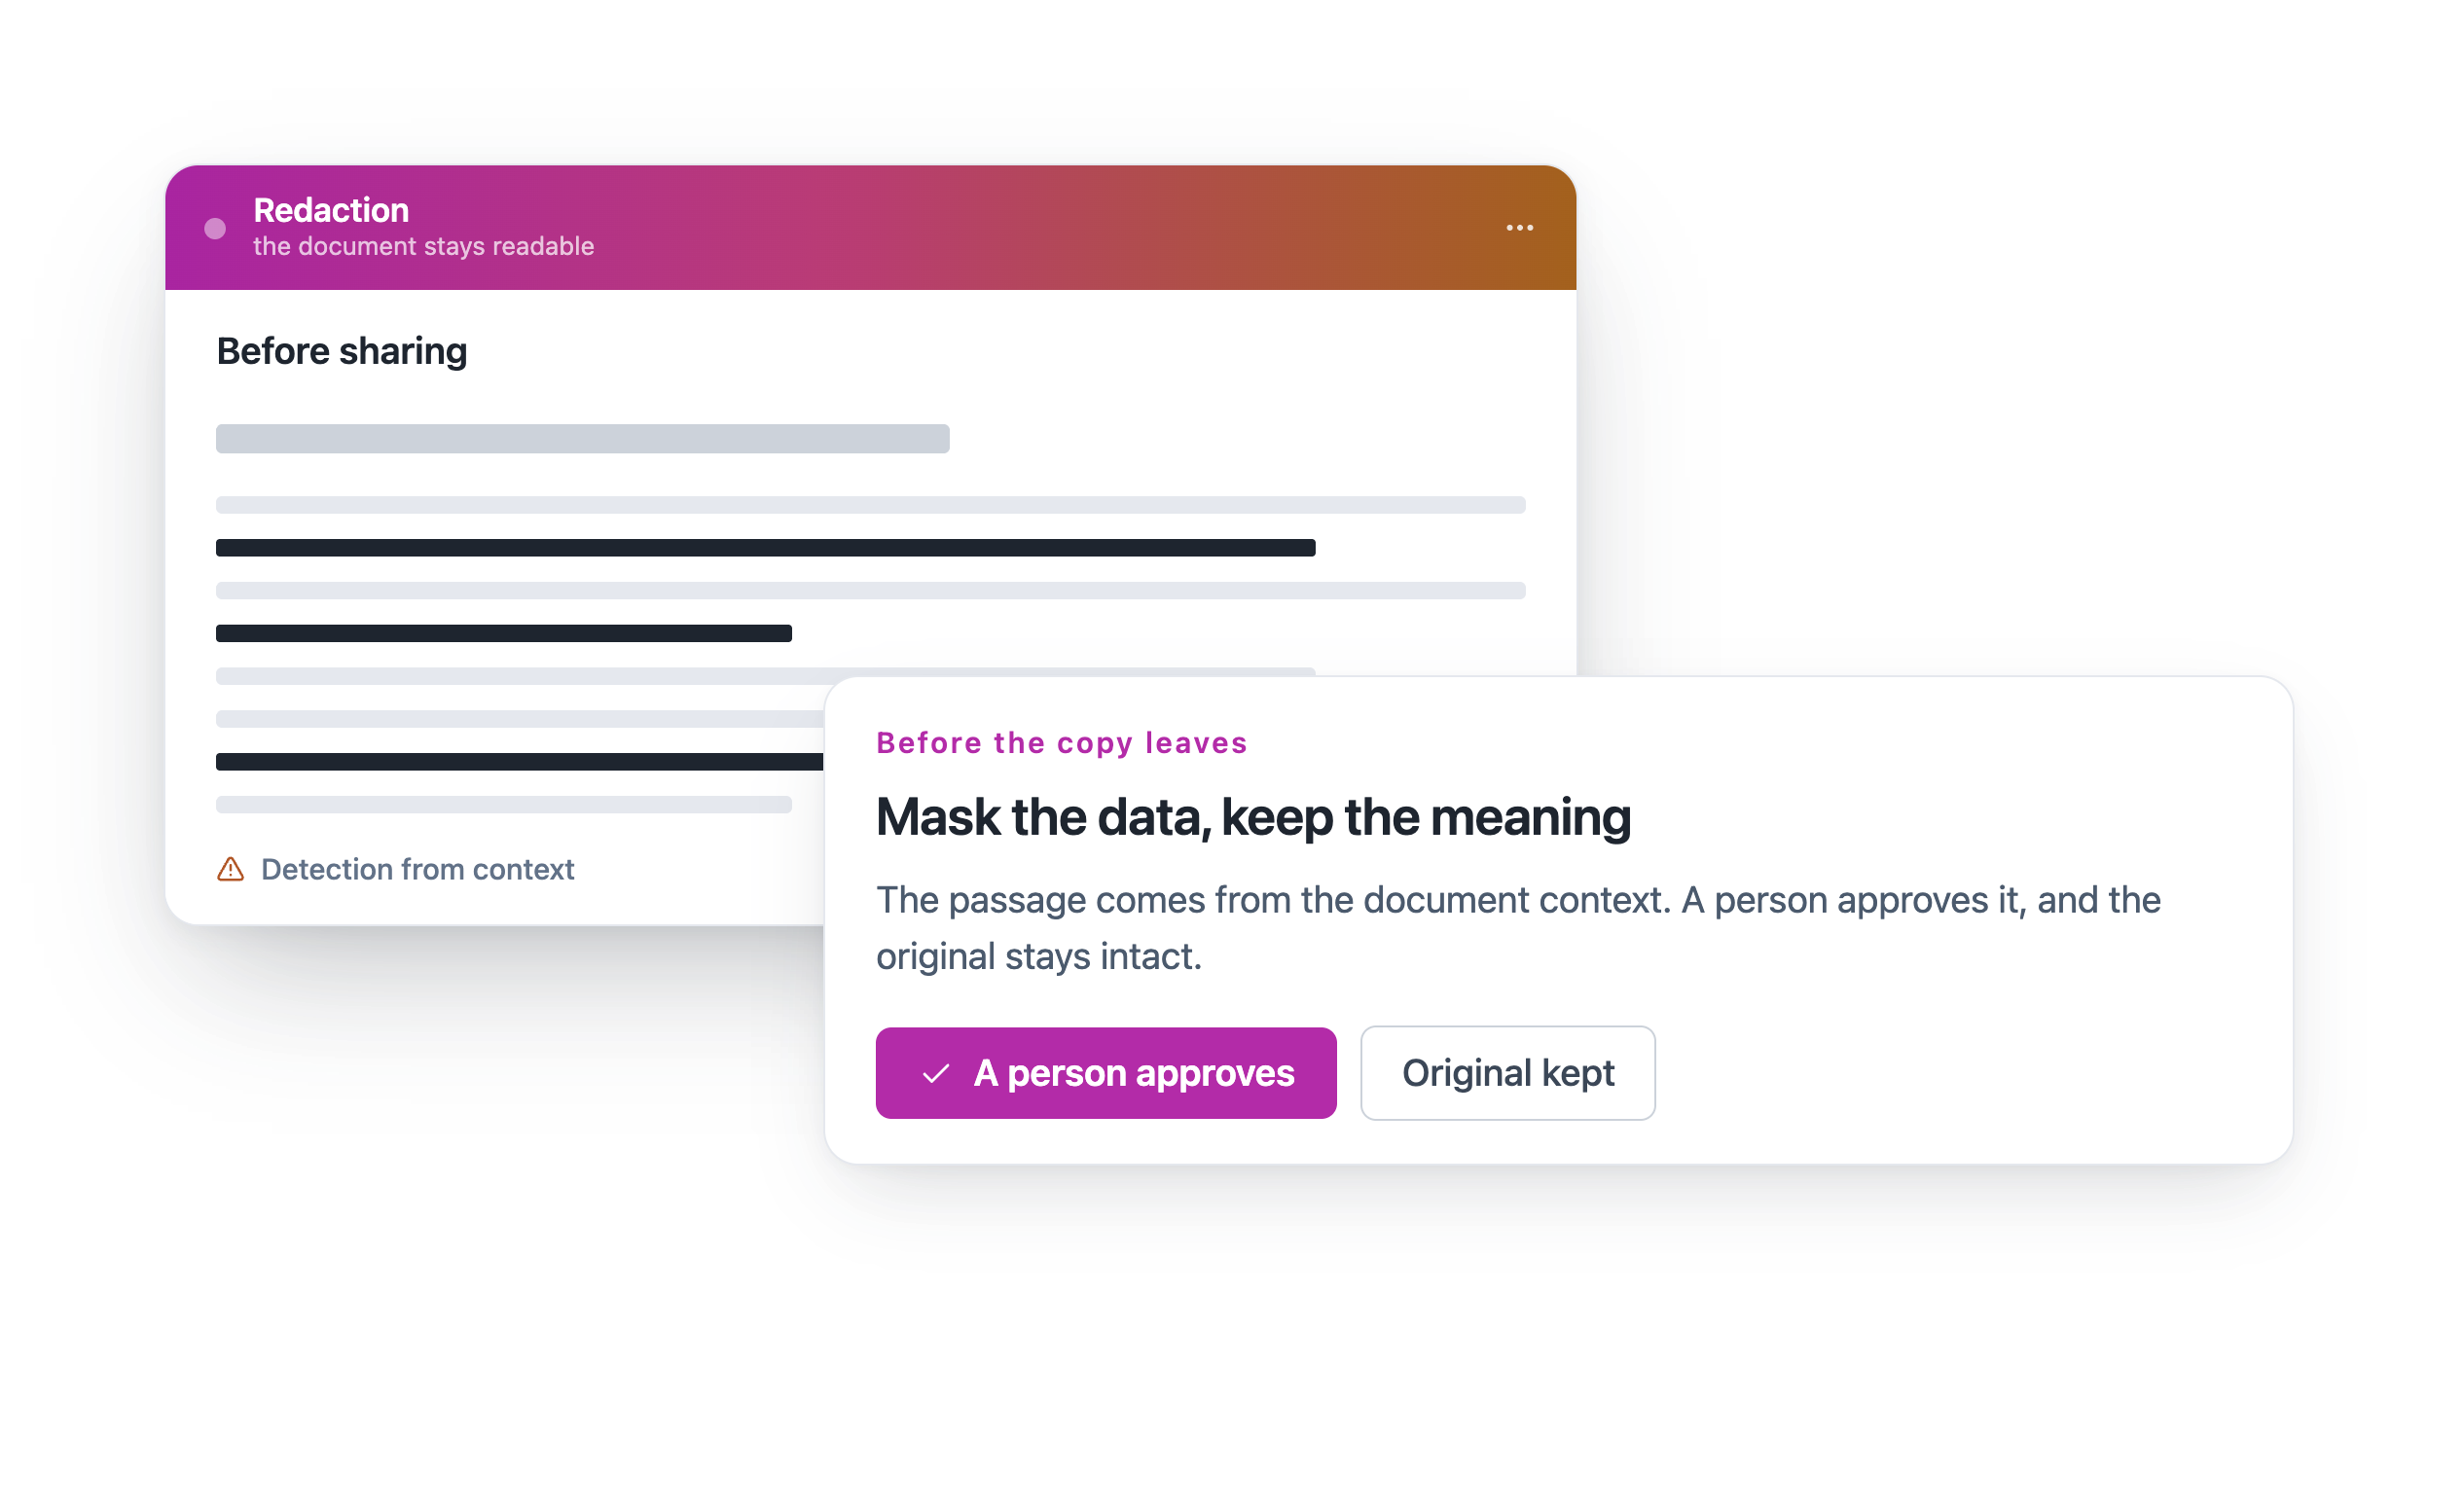
Personal data is rarely contained within a single format. It appears in scanned contracts, correspondence, HR records and legacy archives. Detection and processing happen inside your document workflows, with validation for the cases that require human judgement.
Produce evidence, not merely statements
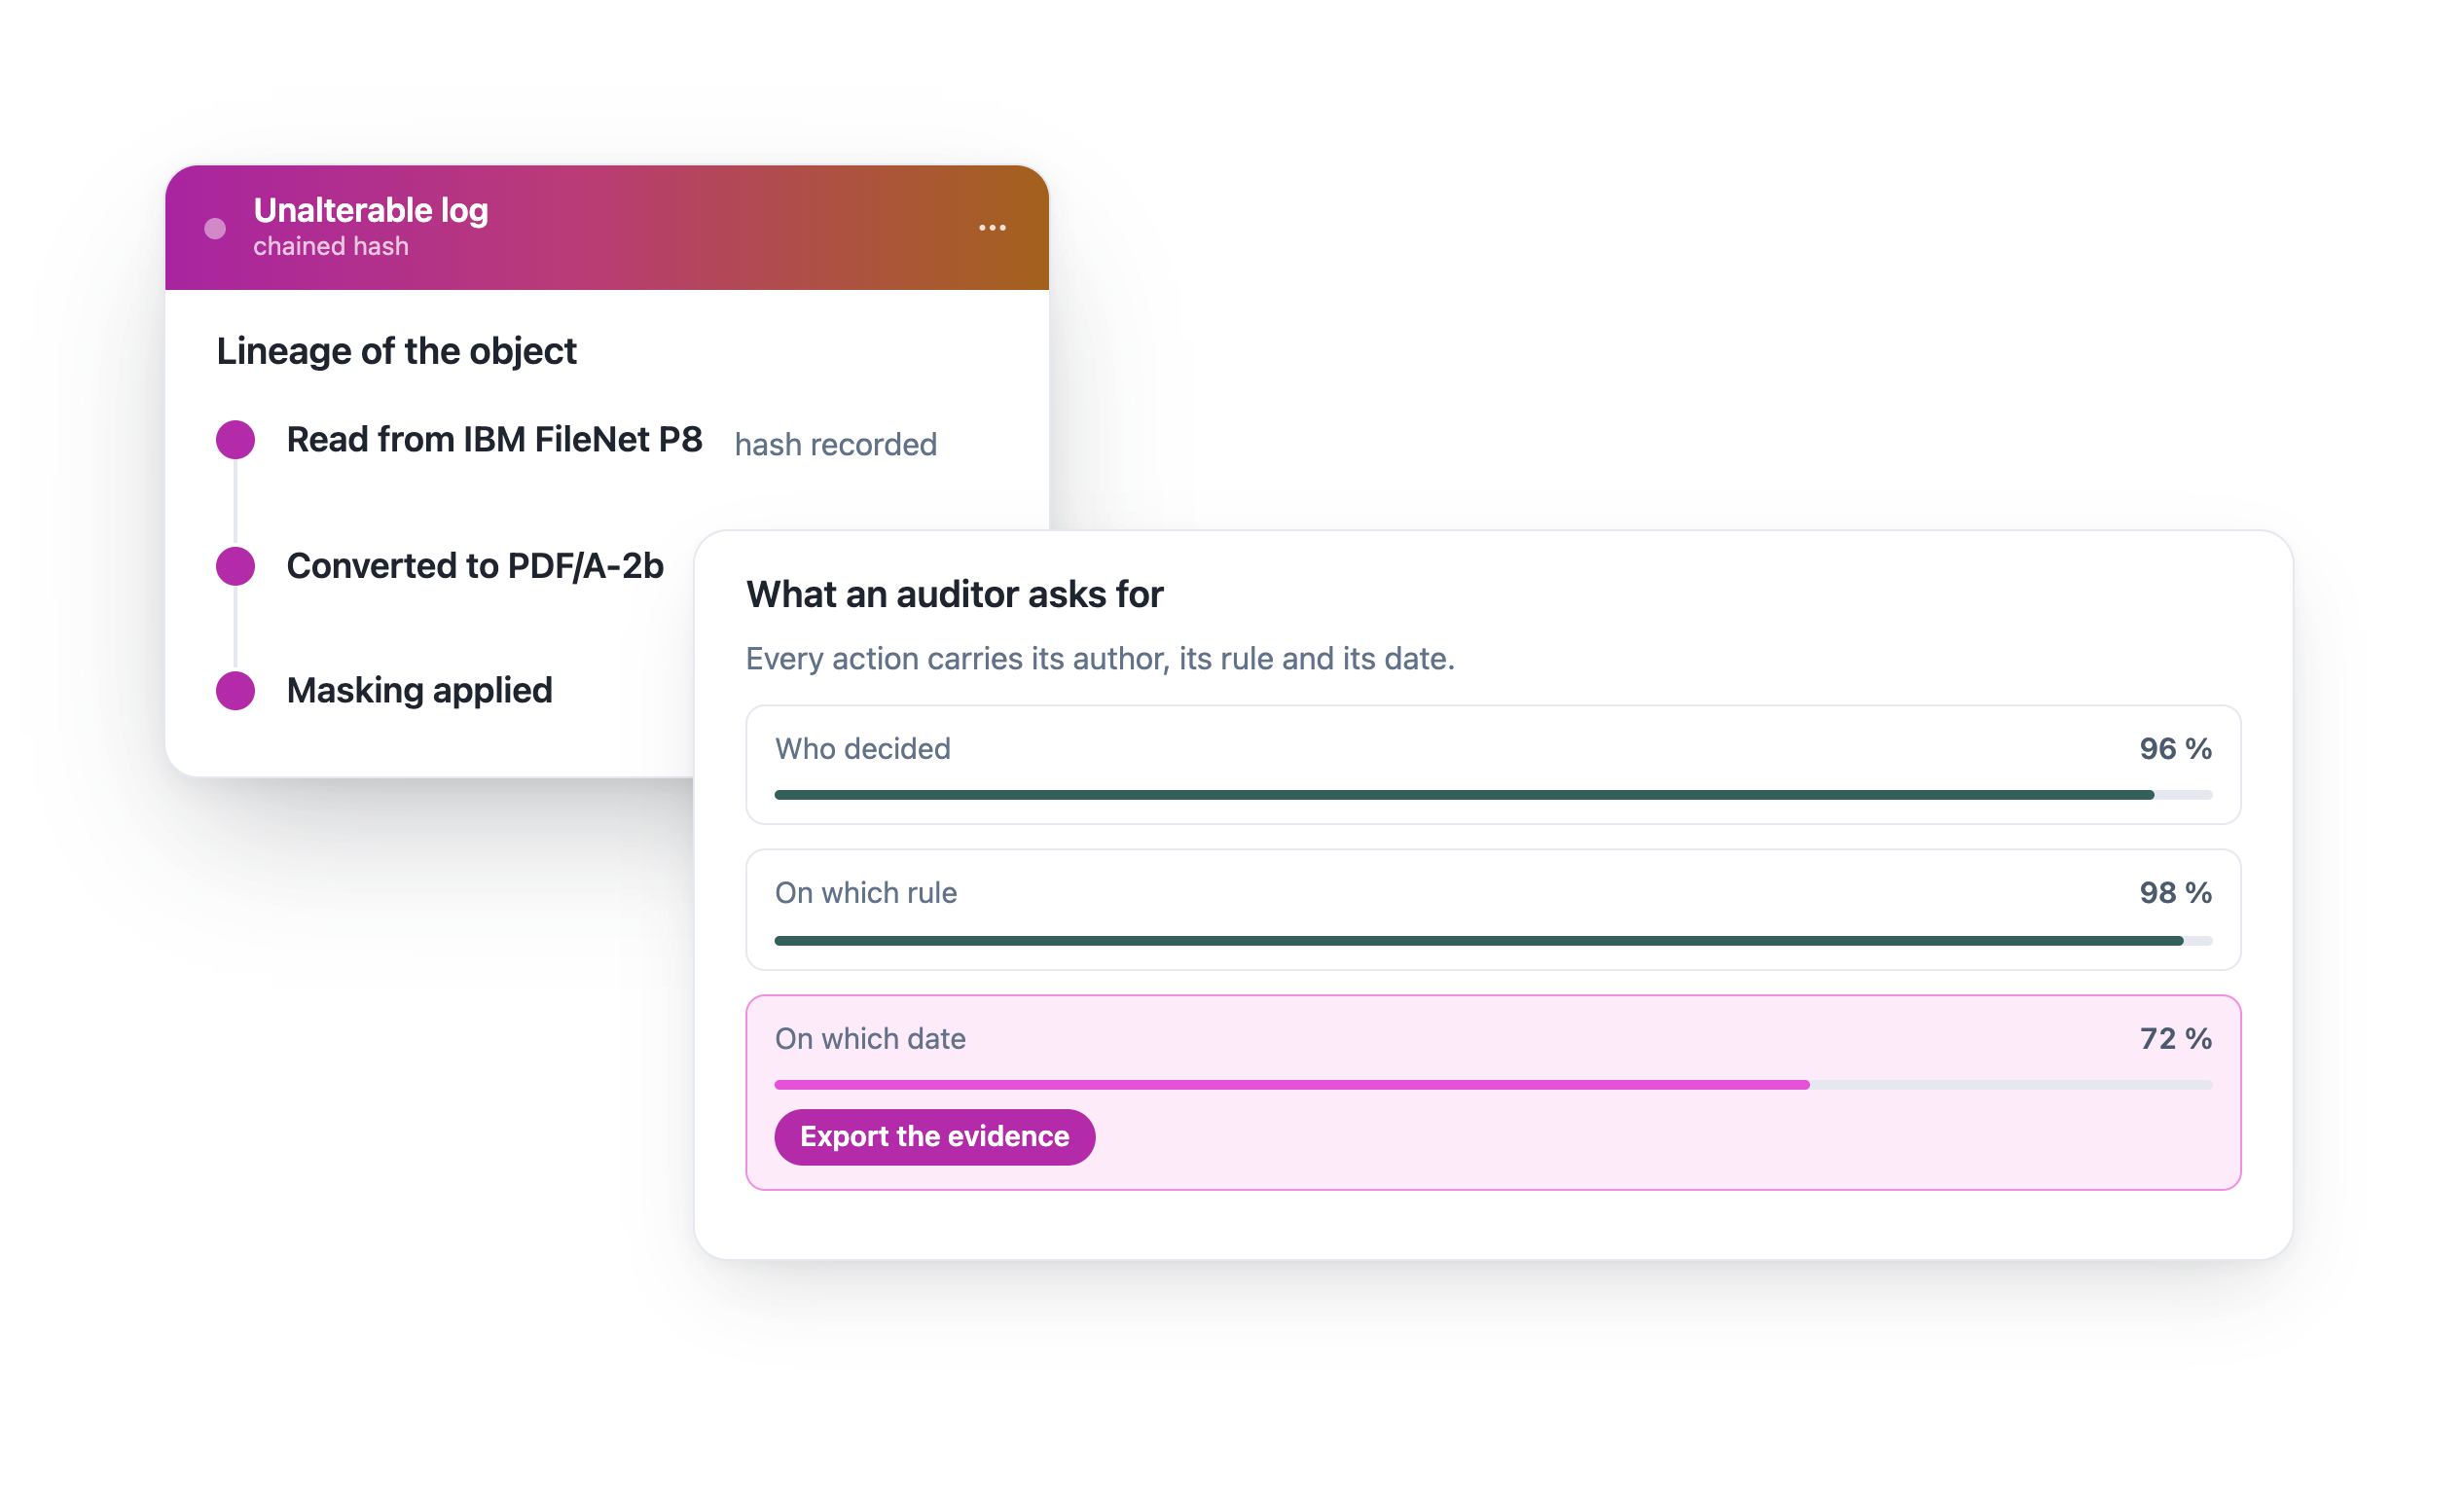
With a regulator or an auditor, it is not enough to state that a policy exists. You show what was classified, which rules were applied, which content was processed, which exceptions were approved and who intervened. Compliance is no longer reconstructed after the event.
Make AI work within your document environment
AI accelerates classification, sensitive data detection, content analysis and the routing of documents into the right workflows. It only creates value when it understands the context of your documents, business rules and existing processes.
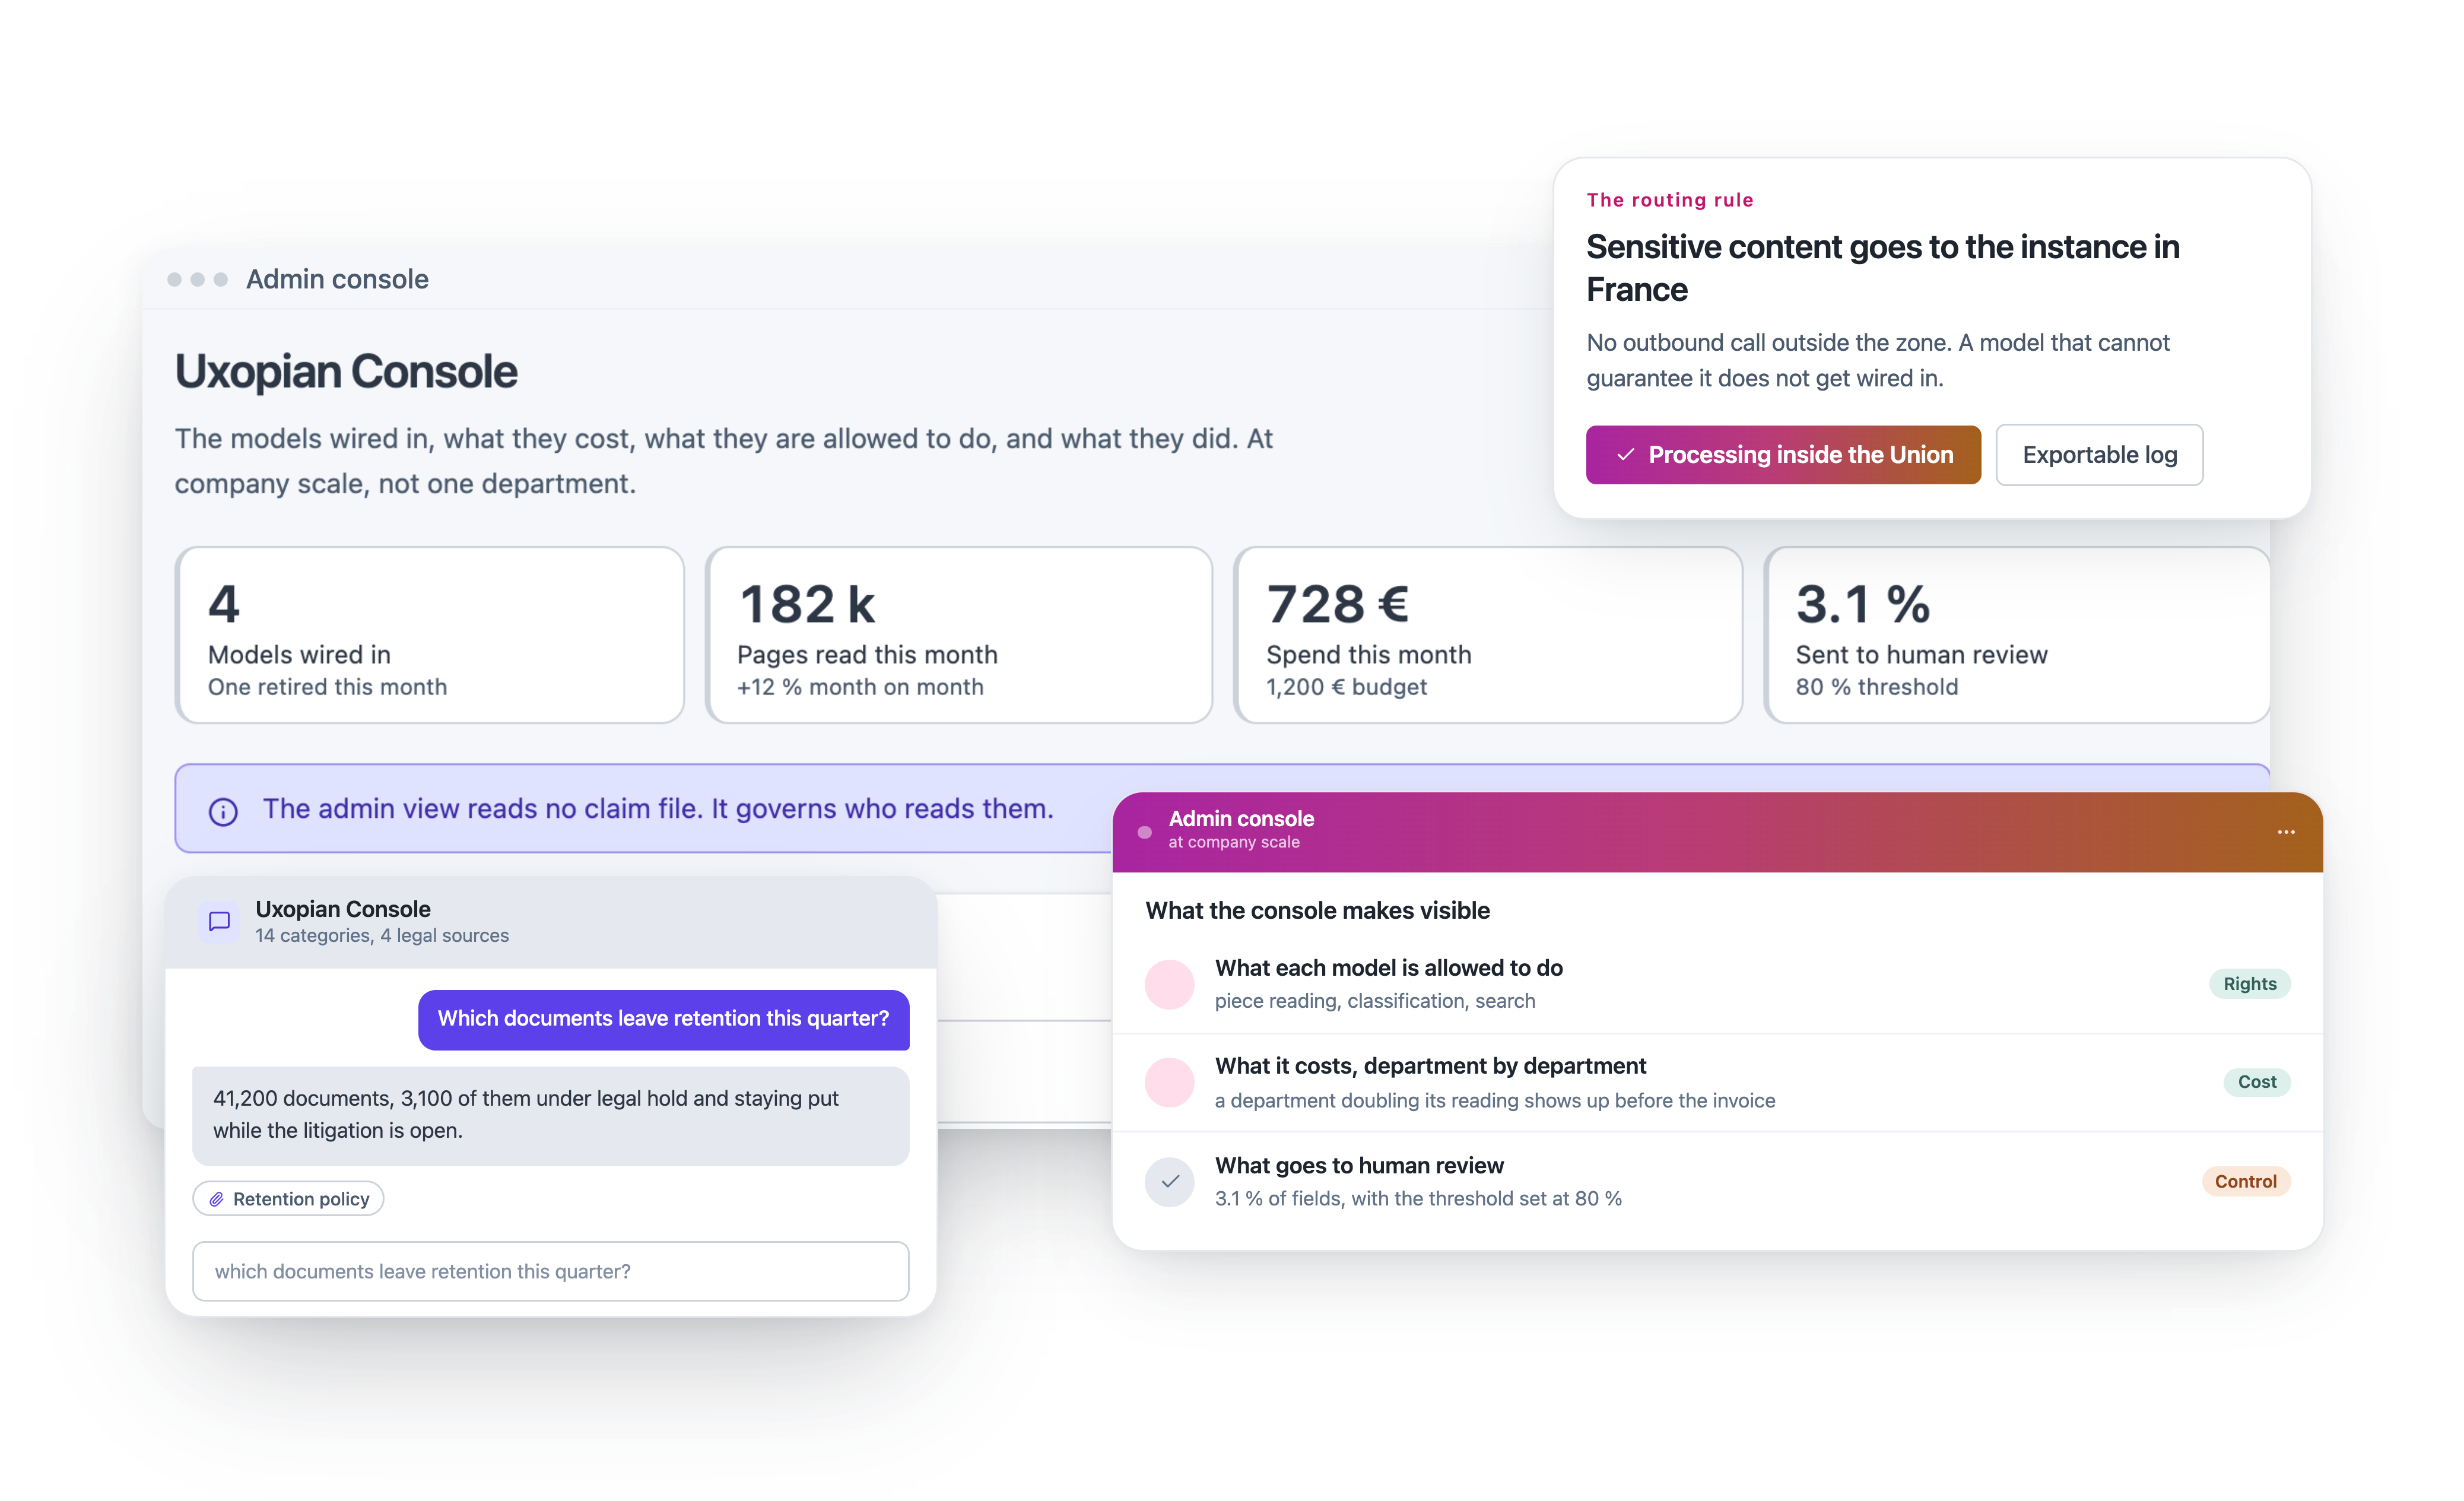
Automate what can be automated. Retain control over decisions that carry consequences for your organisation.
Modernise your governance without rebuilding your information system
Document governance should not become another large-scale transformation programme. Everything sits on your existing infrastructure: legacy document management systems, archives, ECM platforms, business applications, content repositories and hybrid environments.
Four products, one governance foundation
Each one holds a moment of the chain. You do not need all four to start.
Reads the estate in place, transforms the metadata and migrates in batches, with no downtime.
Brings content, business rules and workflows into one case, with its audit trail.
Opens more than two hundred formats with no download, and masks before sharing.
Classifies, detects what is sensitive and prepares the decision, with human validation in the flow.
Where your data lives
On site, private cloud or SaaS. European software. Your data stays on your infrastructure.
Already using our products? The documentation is here.
Governance that supports compliance, IT and business teams
The same foundation, read from four places in the organisation.
For compliance and governance teams
Apply retention policies, improve process traceability and prepare for audits more efficiently.
For IT and information security teams
Modernise content governance without exposing critical data, disrupting operations or creating additional silos.
For business teams
Spend less time searching for, verifying and reconstructing information. Give people content that is clearer, better classified and easier to use.
For executive leadership
Balance operational efficiency, risk management and new AI use cases without losing control of the information estate.
Control is a prerequisite for sustainable transformation
Organisations should not have to choose between innovation and security, automation and traceability, or modernisation and operational continuity. They need document governance that evolves alongside their constraints, regulatory requirements and business practices.
A complex document estate becomes an environment that is easier to understand, better governed and more usable.
Your questions about content governance
What is content governance?
It is the ability to know what your repositories contain, apply your retention and protection rules to it, and prove it. Your rules often exist already: governance makes them run on the content they cover.
It chains four moves: understand your content, apply the rules, protect sensitive data and produce the evidence.
How do you find out what your repositories really contain?
By analyzing content in place, across your document management systems, archives, mailboxes, network drives and business applications. It is classified by type, sensitivity, business value and retention period.
Nothing moves during the scan. The resulting report becomes your work list, and it also prepares a possible ECM migration.
How do you apply retention rules automatically?
By attaching each rule to the content it covers. When the date comes, a workflow triggers a review, an archive, a secure deletion or an extended retention.
A legal hold suspends the planned action. Content is processed by age cohorts and the service stays online throughout.
How do you find and protect personal data scattered across documents?
Personal data hides in scanned contracts, letters, HR files and old archives. Detection starts from the context of the document, beyond a simple word list.
The passage found is redacted, and a person approves before the copy goes out. That is what a data subject access request and stricter GDPR retention scrutiny call for.
What does the AI Act require when AI classifies documents?
The EU AI Act treats some uses as high-risk, such as document classification or personal data detection. Human oversight, explainability and an audit log become obligations.
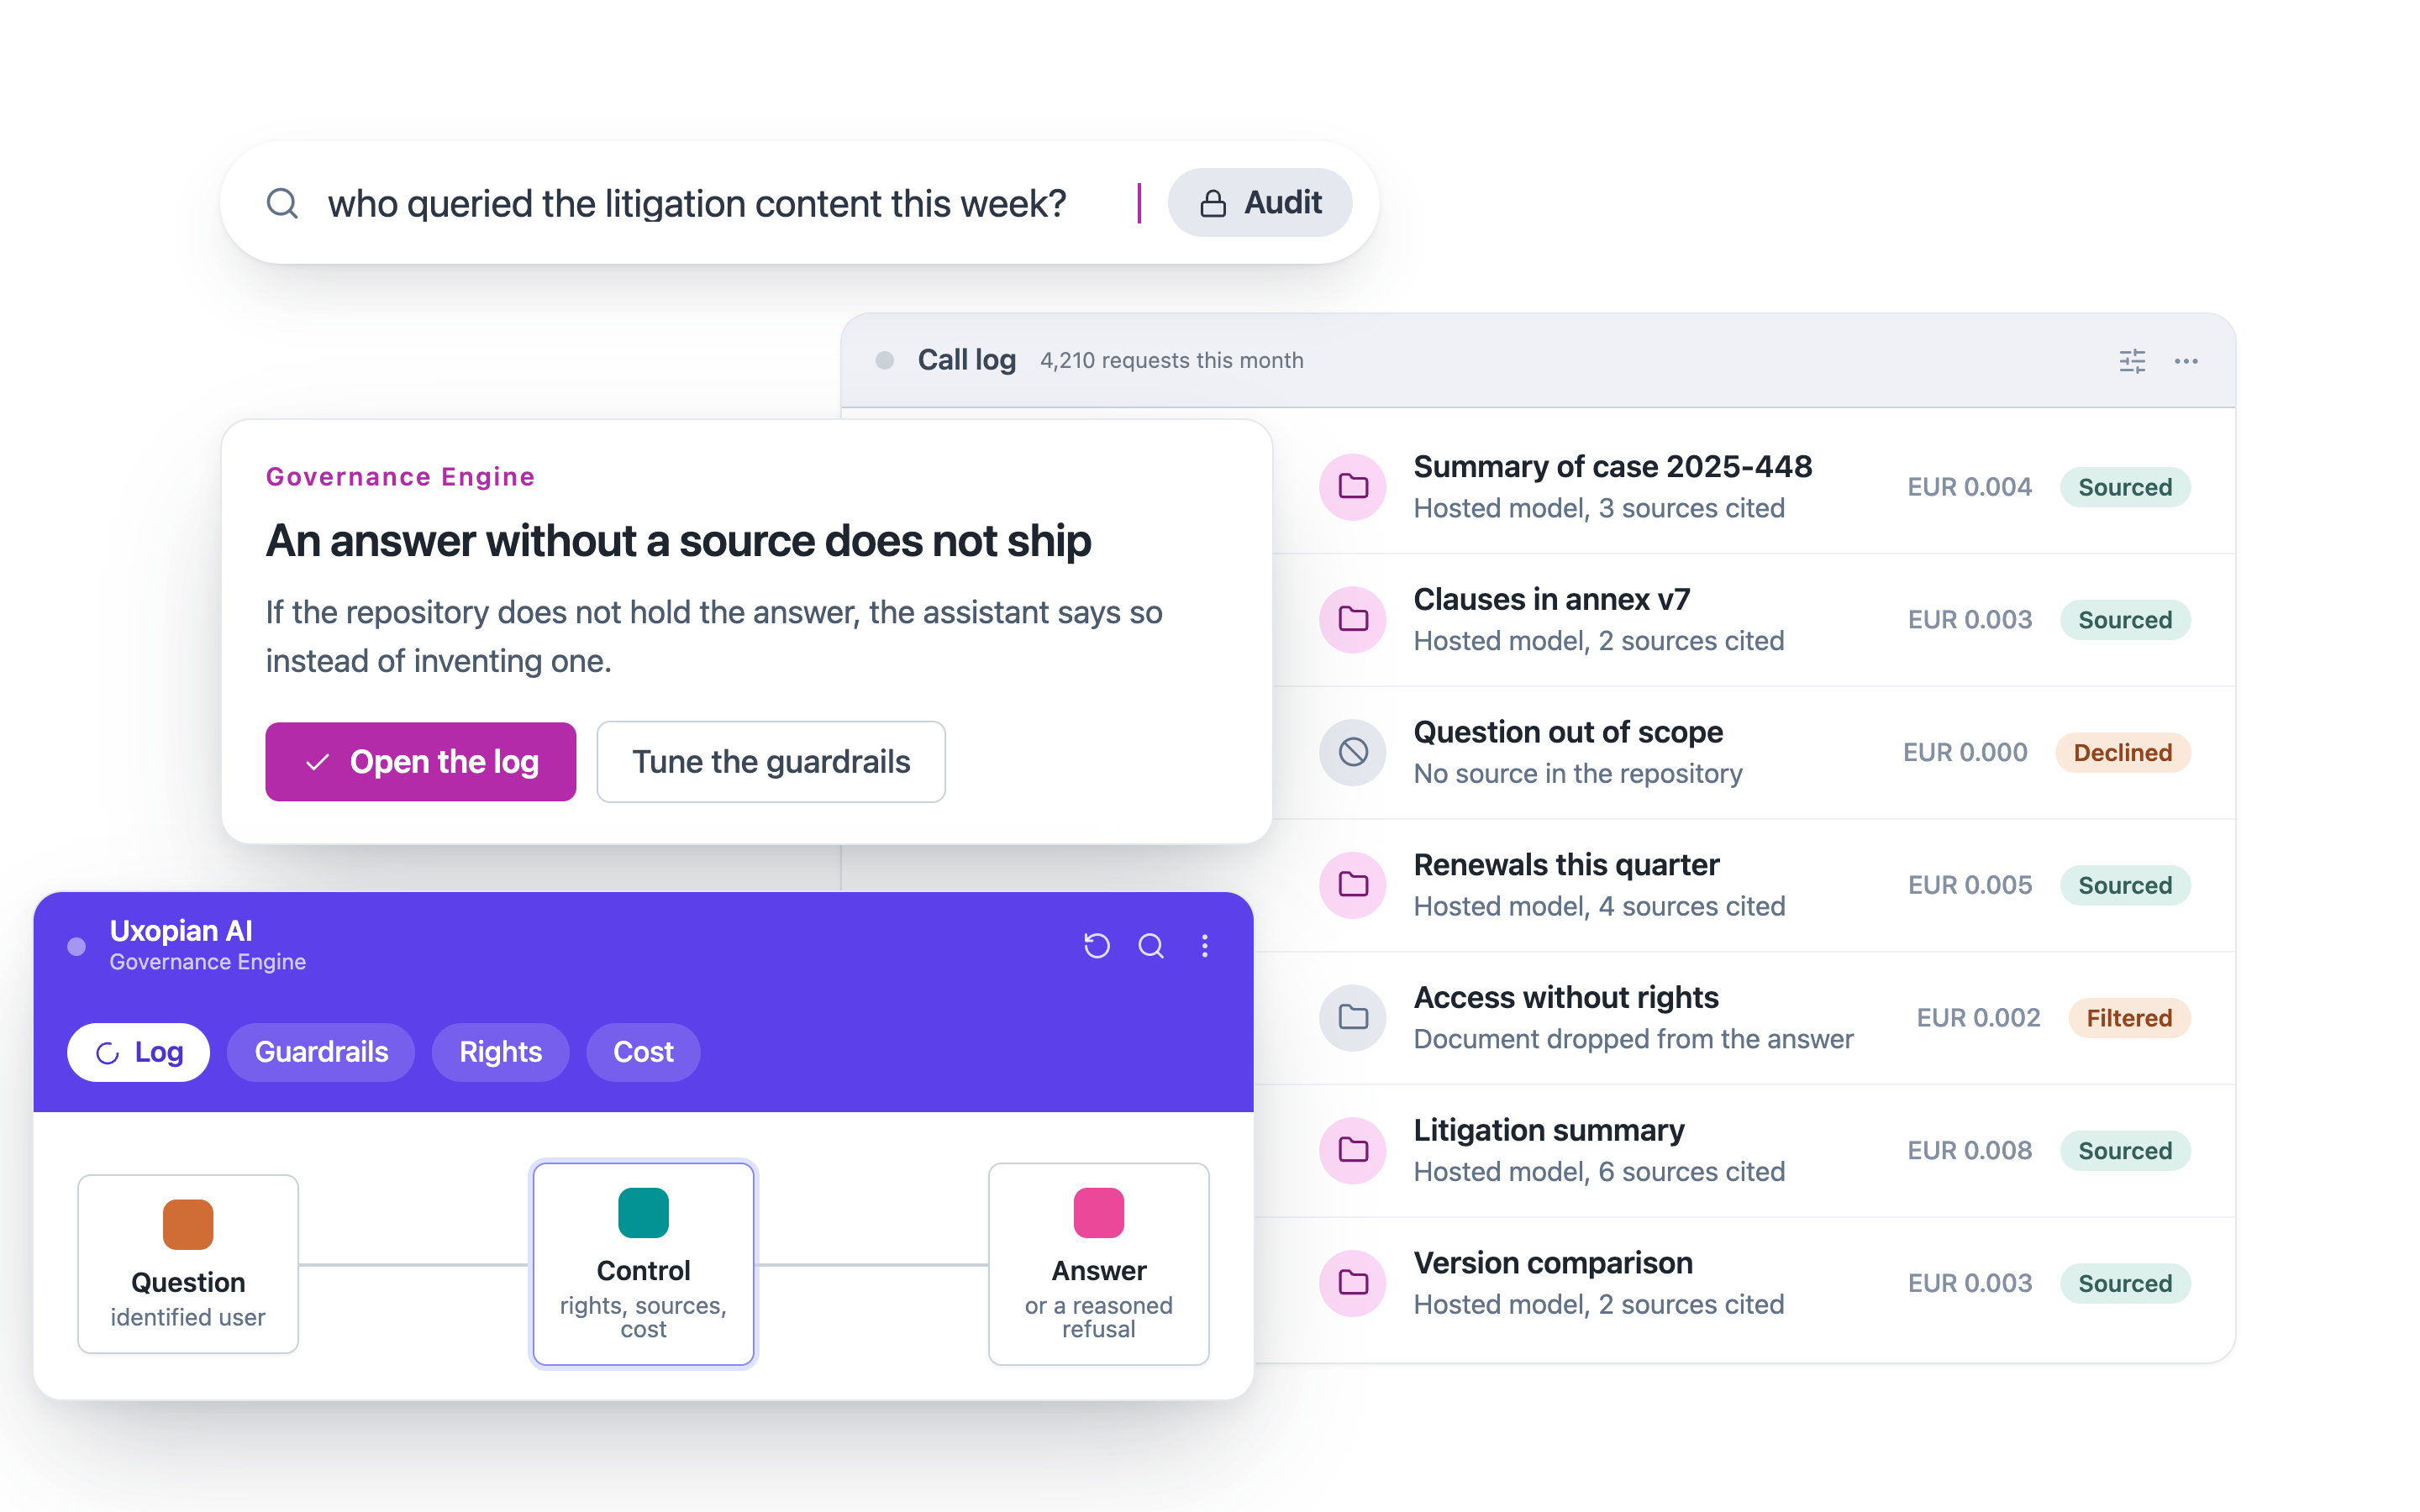
In content governance, the model suggests, a person decides, and the decision stays explainable. Every call is logged. See also AI Guardian.
How do you prove to an auditor that your rules are applied?
By showing what was classified, which rules were applied, which content was processed and by whom. Every action is timestamped and sealed with a chained hash.
The log exports as is. Redacting a piece of personal data shows up just like the final decision.
Do you need to rebuild your information system to govern your content?
No. Everything sits on your current infrastructure: legacy document systems, archives, content platforms, business applications and hybrid environments.
You move forward scope by scope, one document type or use case at a time. The four technologies behind governance are described on the Technology page.
How much content can a governance program handle?
Entire estates. Documents have been consolidated and classified from 30 systems with no loss, and 400 million documents were classified and migrated continuously in fifteen months, across more than 60 entities.
The content operations engine reads content in place, transforms metadata and migrates in batches, with no downtime window.
Do not allow your governance policies to remain unenforced
Thirty minutes on your content, your rules and your deadlines. We look together at what gets classified, what gets disposed of and what gets proven.